In 2023, a cancer patient got a phone call from her hospital: nude photos taken during her radiation treatment had been stolen by hackers and posted to the dark web. She had no idea the photos even existed on the hospital’s network.
The hospital was Lehigh Valley Health Network (LVHN), a nonprofit system operating 13 hospitals and dozens of health centers across eastern Pennsylvania. The attacker was BlackCat (also known as ALPHV), a Russian-speaking ransomware group that had broken into a physician practice’s network supporting radiation oncology imaging.
LVHN refused to pay the ransom demand, reported at the time as in excess of $5 million. BlackCat leaked the images anyway. They included photos of breast cancer patients, taken during clinically appropriate exams, published naked from the waist up on the group’s dark web leak site alongside patient names and diagnoses.[1]
What happened at Lehigh Valley Health Network
The breach was detected on February 6, 2023. A class-action lawsuit followed on March 13, 2023, led by a plaintiff identified only as “Jane Doe” to protect her privacy. It alleged LVHN routinely photographed cancer patients as part of treatment documentation, sometimes without patients being clearly told the images existed or how they were stored, and failed to adequately secure that imaging archive.[2]
- BlackCat breaches the network supporting a Lackawanna County physician practice, compromising a system that stores radiation oncology treatment images.
- LVHN refuses to pay the ~$5M ransom demand. BlackCat leaks roughly 132 GB of stolen data, including nude images of at least three breast cancer patients, to pressure payment. A class-action suit is filed.
- LVHN agrees to a $65 million settlement covering approximately 135,000 affected patients and employees. Plaintiffs’ counsel, Saltz Mongeluzzi Bendesky, described it as the largest settlement of its kind on a per-patient basis in a healthcare data breach or ransomware case.[1]
- Senior Judge Thomas A. James of the Lackawanna County Court of Common Pleas grants final approval. Payouts are tiered: roughly $50 for anyone whose records were merely accessed, up to $70,000–$80,000 for those whose nude images were posted online, and $125,000 for the lead plaintiff.[3]
The leverage was never the file
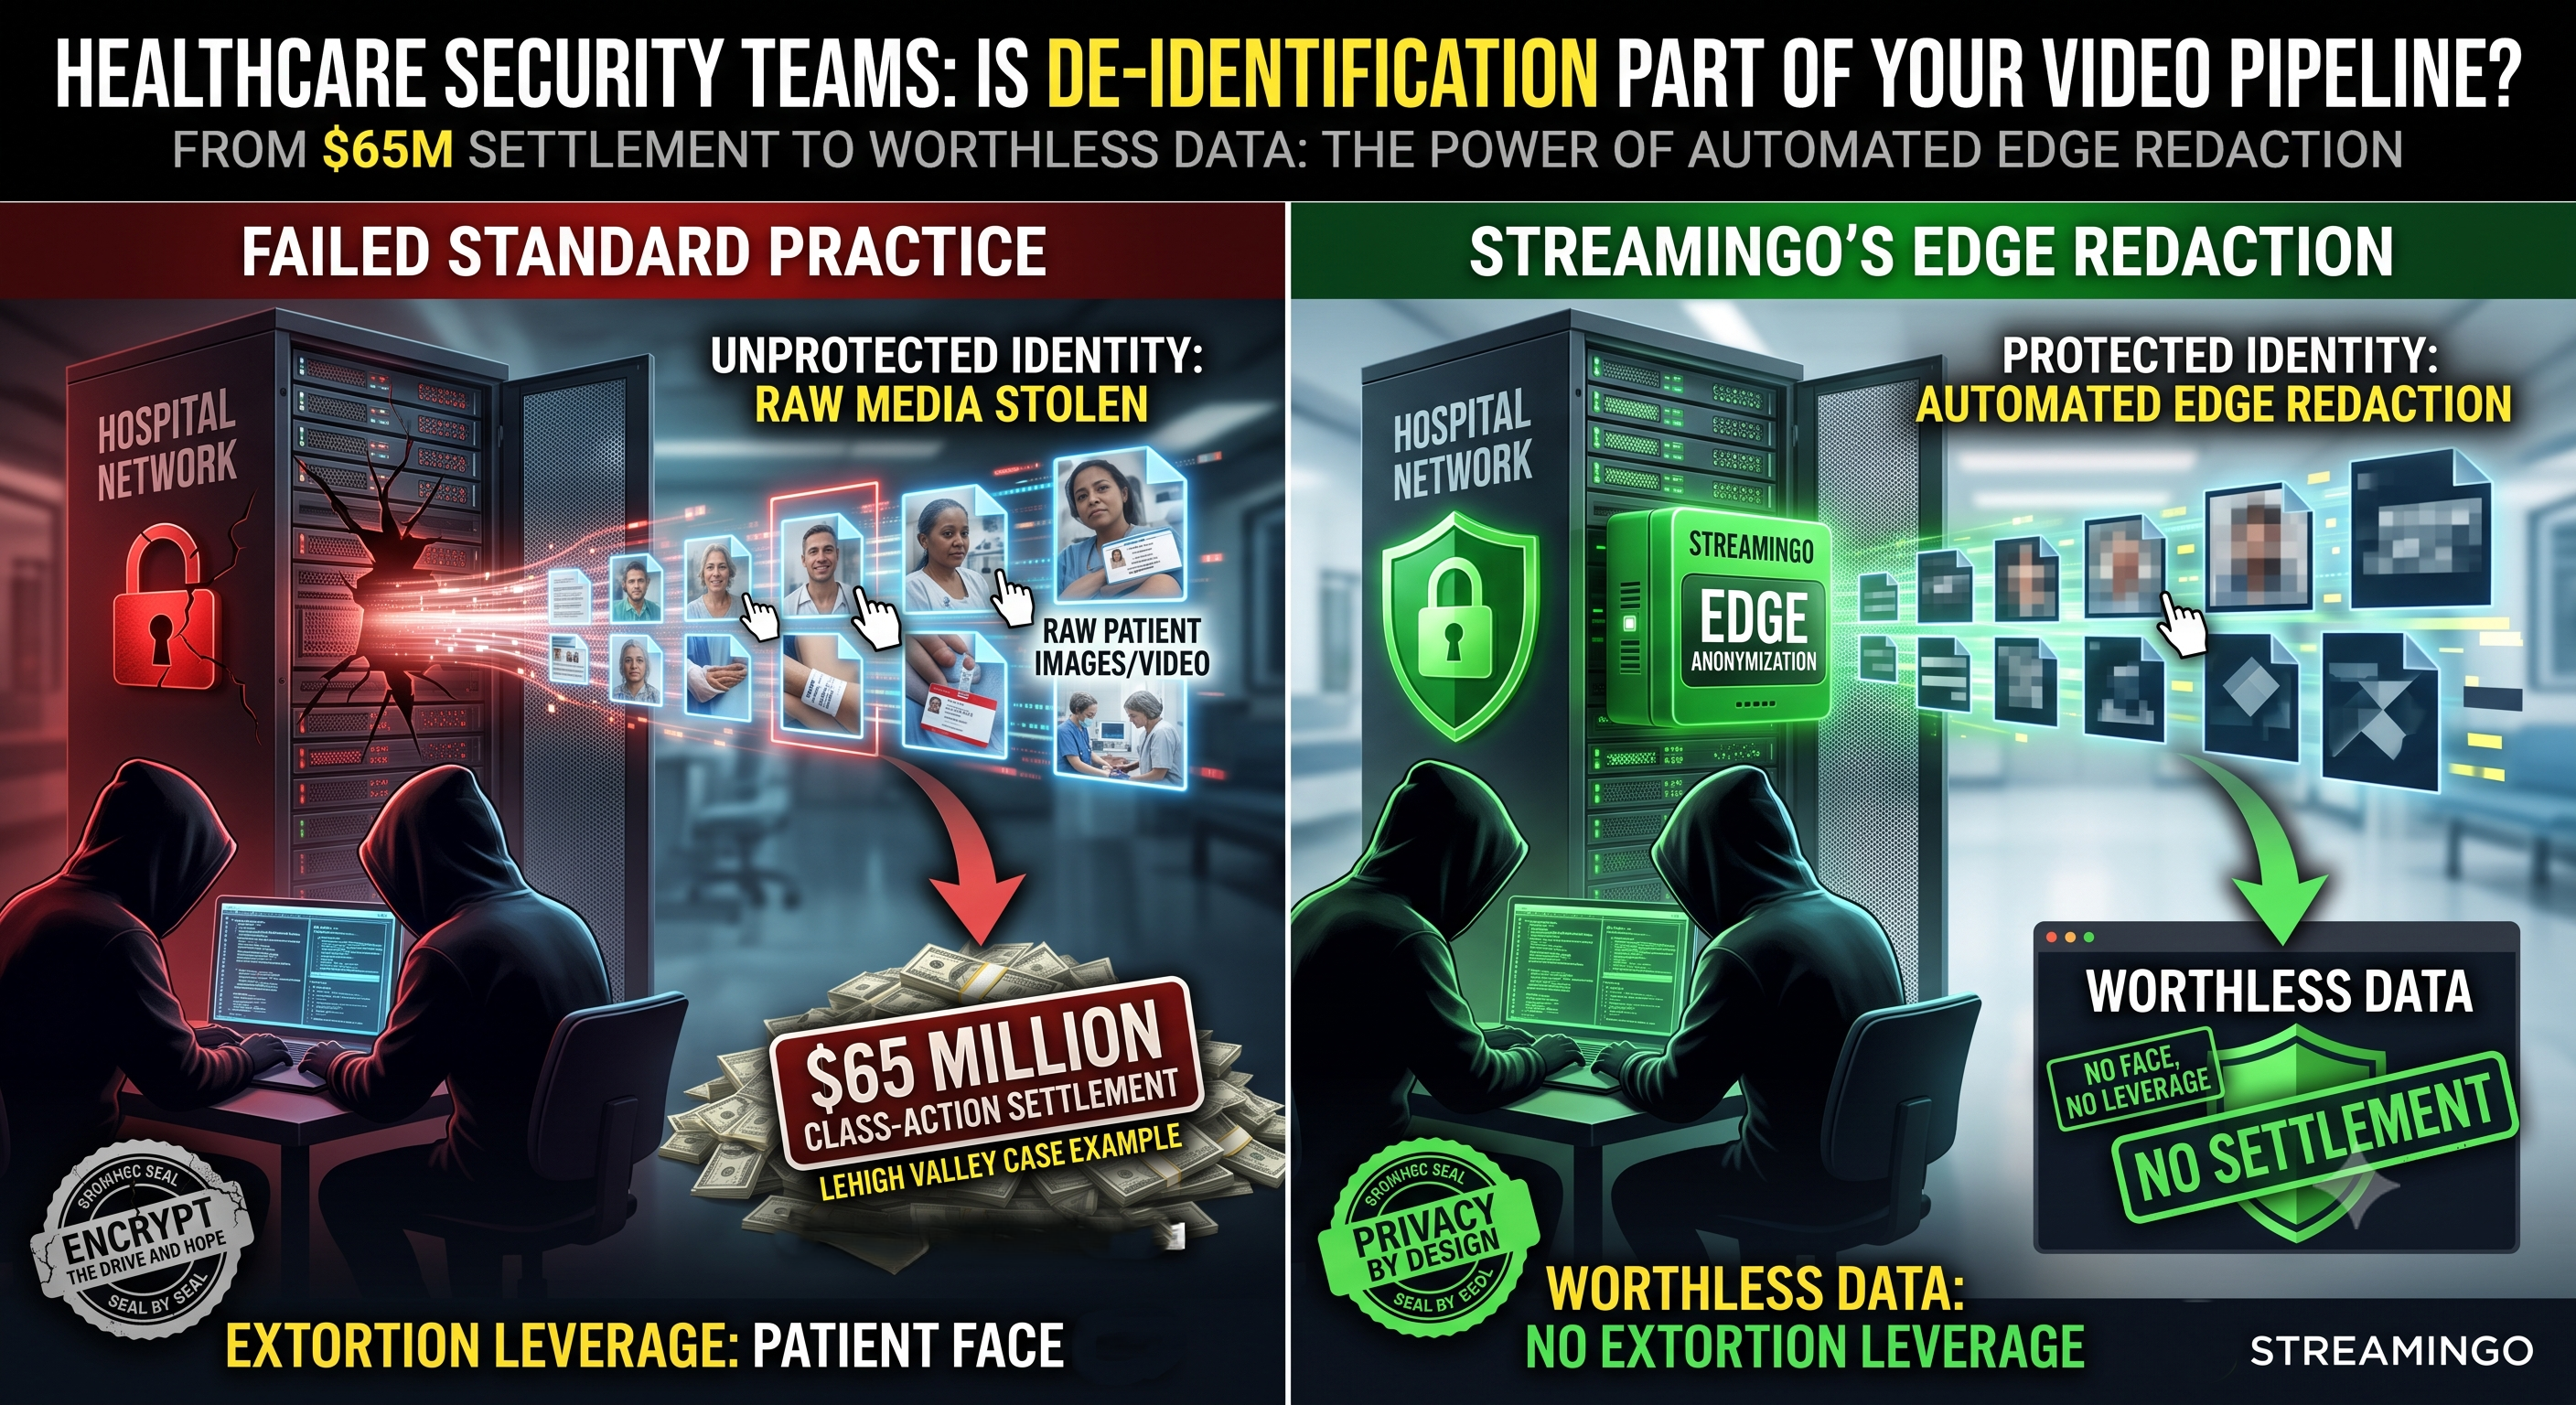
Here is what many information security teams are still missing: the leverage in this attack was never the video or image file itself. It was the patient’s face and identity attached to it.
Take away the identity, and the same footage becomes worthless to extort with. No face to threaten someone with. No name to attach to a diagnosis. No leverage, and in all likelihood no six-figure settlement.
This is the mechanism most breach post-mortems miss. Encryption protects a file from being read in transit or at rest, but once it is decrypted for legitimate clinical use, the identity is fully intact and fully exploitable if that copy is ever exfiltrated. Access controls limit who can open a file, and they do nothing once an attacker is already inside the perimeter. Neither approach touches the actual asset being weaponized: the identifiable human being in the frame.
A different security posture
That reframing implies a fundamentally different posture than “encrypt the drive and hope.” It means treating de-identification as a workflow requirement for any clinical imaging or video, not a compliance checkbox applied after the fact and not a manual redaction step queued up for whenever staff have time.
Afterthought approach
Identity stored, then defended
- Full-face clinical imagery stored indefinitely on shared network drives
- Identity protected only by perimeter security and access lists
- A single breach exposes every identifiable image at once
- Extortion leverage exists for as long as the files exist
Pipeline approach
Identity removed at ingestion
- Faces are irreversibly de-identified before footage is stored
- Clinical and behavioral detail (positioning, treatment area, timing) is preserved for care and research
- A breach of the archive yields no identifiable images to leak
- There is no face left to threaten a patient with
How Streamingo fits into the pipeline
This is the problem we built Streamingo Anonymize to solve. It is our GDPR-compliant video redaction module, with automated de-identification built into surgical and clinical video pipelines. It strips identity at the edge, before footage ever sits exposed on a server waiting to be exfiltrated.
In practice, facial de-identification happens as part of ingestion, not as a separate project bolted on after a near-miss or an actual breach. Treatment documentation, surgical recordings, and radiation oncology imaging can still support clinical review, quality audits, and research. The behavioral and procedural detail stays fully intact, but the one data point that turns a stolen file into extortion leverage is never stored in the first place.
For the regulatory side of this approach, see our guide to a unified framework for video PII compliance across GDPR, HIPAA, CCPA and DPDP.
The question for your team
LVHN’s leadership has said patient and staff privacy remain a top priority and that its defenses have been enhanced since the attack. That is the right response after the fact. The harder question is the one every healthcare security team should ask before the fact:
The file was never really the asset worth stealing. The identity attached to it was. Once a security team internalizes that distinction, the roadmap for where to invest (encryption, access control, or identity removal at the edge) starts to look very different.